

ISACA CISM-JPN exam dumps : Certified Information Security Manager (CISM日本語版)
- Exam Code: CISM-JPN
- Exam Name: Certified Information Security Manager (CISM日本語版)
- Updated: Oct 13, 2026 Q & A: 1193 Questions and Answers

 PDF Version Demo

PC Test Engine
ISACA CISM日本語 Value Pack (Frequently Bought Together)

- If you purchase ISACA CISM日本語 Value Pack, you will also own the free online test engine.
- PDF Version + PC Test Engine + Online Test Engine
- Value Pack Total: $139.98 $89.99
About ISACA CISM日本語 Exam
In 2026, a stale question bank is a liability. PracticeTorrent includes 365 days of free updates with every CISM日本語 purchase and notifies you the moment a new version is released, so your ISACA Certified Information Security Manager (CISM日本語版) prep never falls behind the exam.
ISACA CISM日本語 Exam Overview:
| Certification Vendor: | ISACA |
|---|---|
| Exam Name: | Certified Information Security Manager |
| Exam Number: | CISM |
| Real Exam Qty: | 150 |
| Related Certifications: | CISM |
| Exam Price: | $575 (Member) / $760 (Non-Member) |
| Passing Score: | 450 (out of 800) |
| Exam Format: | Multiple Choice |
| Exam Duration: | 240 minutes |
| Available Languages: | Japanese, Spanish, English, Chinese-Simplified, German, French |
| Certificate Validity Period: | 3 years (requires maintenance fees and CPE) |
| Sample Questions: |  |
| Exam Way: | Computer-based testing at authorized PSI testing centers or remotely proctored. |
| Pre Condition: | To earn the CISM certification, candidates must pass the exam and possess a minimum of five years of information security work experience with a minimum of three years of information security management work experience in three or more of the CISM domains. Substitutions and waivers for general information security experience are available. |
| Official Syllabus URL: | https://www.isaca.org/credentialing/cism |
ISACA CISM日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Information Security Risk Management | 20% | - Integrate risk management into business and IT processes - Identify and/or recommend risk treatment options - Evaluate information security controls to determine whether they are appropriate and effectively mitigate risk - Establish and/or maintain a process for information asset identification, classification, risk assessment and ownership - Monitor and communicate the information security risk posture - Determine appropriate risk treatment options - Identify legal, regulatory, organizational and other applicable compliance requirements - Ensure that risk assessments, vulnerability assessments and threat assessments are performed consistently, at appropriate times, and to identify acceptable risk |
| Information Security Program Development and Management | 33% | - Establish and maintain information security architectures (people, process, technology) - Develop and maintain a security awareness, training and education program for all stakeholders - Align the information security program with the operational objectives of other business functions - Establish, communicate and maintain organizational information security standards, guidelines, procedures and other documentation - Integrate information security requirements into organizational processes - Identify, acquire and manage information security requirements for internal and external resources (services, partners, and suppliers) - Monitor and manage the information security program - Establish and/or maintain the information security program in alignment with the information security strategy |
| Information Security Incident Management | 30% | - Establish and maintain incident escalation and notification processes - Develop and implement processes to ensure the timely identification of information security incidents - Organize, train and equip teams to effectively respond to information security incidents - Test, review and revise the incident response plan - Establish and maintain an incident response plan to ensure an effective and timely response to information security incidents - Establish and maintain an organizational definition of, and severity hierarchy for, information security incidents - Establish and maintain processes to investigate and document information security incidents - Establish and maintain communication plans and processes to manage communication with internal and external entities |
| Information Security Governance | 17% | - Establish and/or maintain information security policies to guide the development of standards, procedures and guidelines in alignment with enterprise goals and objectives - Establish and/or maintain an information security governance framework and supporting processes to ensure that the information security strategy is aligned with the goals and objectives of the organization - Define and communicate the roles and responsibilities for information security throughout the organization - Establish, monitor, evaluate and report information security management metrics - Obtain commitment from senior management and other stakeholders for the information security program - Identify internal and external influences to the organization that affect the information security strategy and program - Develop business cases to support investments in information security |
Key Facts About the CISM日本語 Exam and PracticeTorrent's Service
The current exam information lists 150 questions for the CISM日本語 exam, with 240 minutes minutes allowed. Practicing against the clock at home builds the pacing habits that exam day rewards.
The ISACA Certified Information Security Manager (CISM日本語版) blueprint covers these main domains:
- Information Security Governance (17%)
- Information Security Risk Management (20%)
- Information Security Incident Management (30%)
Additional domains complete the official outline, and our bank covers the full range.
Your money is protected by clear conditions. If you fail the corresponding exam within 60 days of purchase, send us a scanned copy of your enrollment slip and your official Score Report PDF within two days of the exam date; verified claims receive a full refund within seven days. The exclusions: exams taken within three days of purchase, a candidate name that does not match the payer, and free or expired products. If you prefer, we can exchange your product for two others of equal value instead.
ISACA lists the following prerequisites for the ISACA Certified Information Security Manager (CISM日本語版): To earn the CISM certification, candidates must pass the exam and possess a minimum of five years of information security work experience with a minimum of three years of information security management work experience in three or more of the CISM domains. Substitutions and waivers for general information security experience are available..
Check the official certification page for the latest requirements before booking.
Because we remove the guesswork at every step. The CISM日本語 bank consolidates the ISACA Certified Information Security Manager (CISM日本語版) knowledge points into expert-verified Q&As instead of leaving you to sift through the internet alone. A free demo shows the quality before you buy; instant delivery starts you the minute you do; 365 days of free updates — with a notification each time a new version releases — keep you current; and a strict information safety system plus a 7/24 golden-standard support team protect you throughout.
As of the latest information, the CISM日本語 exam requires a score of 450 (out of 800) to pass, and registration costs $575 (Member) / $760 (Non-Member). ISACA sets both figures, so verify them on the official site when you book.
Upon successful payment, our system automatically emails the product to your mailbox and shows an instant download link — delivery typically takes about a minute. If nothing arrives within two hours, check your spam folder first, then contact our 7/24 support team. Installations are unlimited. Your purchase also includes 365 days of free updates: whenever we release a new version, we notify you to download it — no need to wait or worry about validity — and a 50% renewal discount applies when the period ends.
ISACA Certified Information Security Manager (CISM日本語版) Sample Questions:
以下の人物のうち、リスク許容度に基づいたリスク受容の決定について責任を負うのに最も適任なのは誰ですか?
- A. 情報セキュリティ運営委員会
- B. 情報セキュリティマネージャー
- C. リスク所有者
- D. 最高リスク責任者(CRO)
Correct Answer: C 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
情報セキュリティ予算の配分方法を決定する際に、以下のうち最も重要なのはどれですか?
- A. 事業影響評価
- B. 規制遵守基準
- C. 情報セキュリティポリシー
- D. 情報セキュリティ戦略
Correct Answer: D 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
組織の情報セキュリティポリシーを策定する際に、最も重要な考慮事項は次のうちどれでしょうか?
- A. 経営陣はこれらの方針を支持しています。
- B. 職務内容には、セキュリティポリシーを読むことが求められます。
- C. これらのポリシーは業界のベストプラクティスに準拠しています。
- D. ポリシーは毎年更新されます。
Correct Answer: A 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
組織の自動セキュリティ監視ツールが、過剰に大量の誤検知を生成しています。監視プロセスを最適化するための最適な方法は次のうちどれですか?
- A. ログ記録を再設定します。
- B. 特定の時間枠内で発生した事象を監視します。
- C. 重大なアラートのみを報告します。
- D. 変更報告のしきい値。
Correct Answer: D 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
IT統制の運用有効性を確保する主要な責任を負う役割は、次のうちどれですか?
- A. コントロールテスター
- B. 情報セキュリティマネージャー
- C. リスク所有者
- D. ITコンプライアンスリーダー
Correct Answer: B 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
Viewing page 1 out of 239 pages.
Viewing questions 1-5 out of 1193 questions.


Related Exams
Related Certifications
Over 81356+ Satisfied Customers
What Clients Say About Us
Why Choose Us
-
QUALITY AND VALUE
PracticeTorrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
-
TESTED AND APPROVED
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
-
EASY TO PASS
If you prepare for the exams using our PracticeTorrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
-
TRY BEFORE BUY
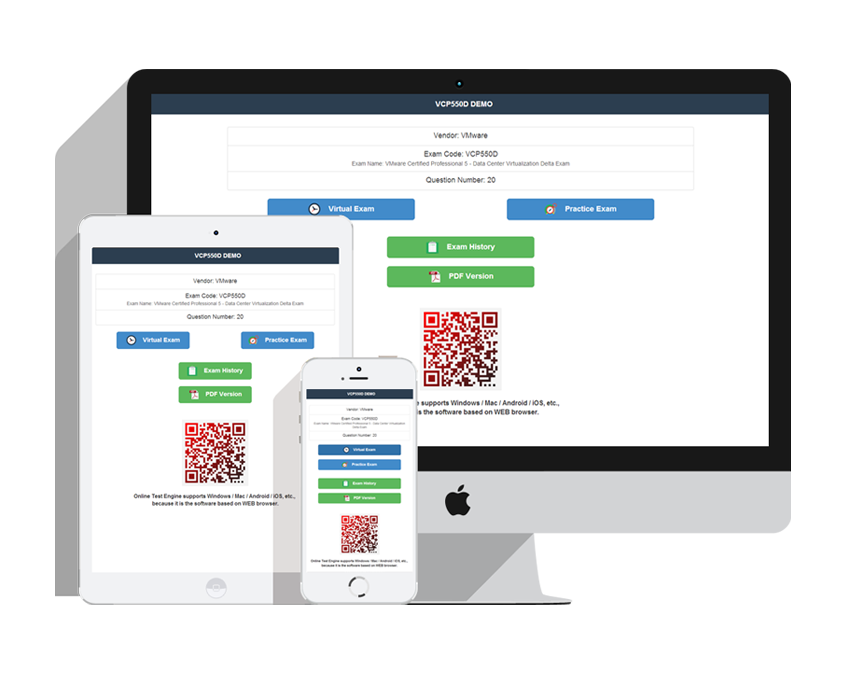
PracticeTorrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
Our Clients




Get the high score and achieve the certification with our latest practice torrent. The complete exam prep torrent contains the questions & answers which are related to the actual test. You can pass your actual test at first attempt.
Tags
- AIGP practice torrentMay 28, 2022
- SC-100J practice torrentMay 28, 2022
- CBM practice torrentMay 28, 2022
- CFE-Fraud-Prevention-and-Deterrence practice torrentMay 28, 2022
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PracticeTorrent NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy