


Use MS-100 Exam Dumps (2023 PDF Dumps) To Have Reliable MS-100 Test Engine
MS-100 PDF Recently Updated Questions Dumps to Improve Exam Score
NEW QUESTION # 49
Your company has a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
You sign up for Microsoft Store for Business.
The tenant contains the users shown in the following table.
Microsoft Store for Business has the following Shopping behavior settings:
* Allow users to shop is set to On.
* Make everyone a Basic Purchaser is set to Off.
You need to identify which users can install apps from the Microsoft for Business private store.
Which users should you identify?
- A. user1, User2, User3, User4, and User5
- B. User1, User2, User3, and User4 only
- C. User1 only
- D. User3 and User4 only
- E. User1 and User2 only
Answer: E
Explanation:
Explanation
Allow users to shop controls the shopping experience in Microsoft Store for Education. When this setting is on, Purchasers and Basic Purchasers can purchase products and services from Microsoft Store for Education.
References:
https://docs.microsoft.com/en-us/microsoft-store/acquire-apps-microsoft-store-for-business
NEW QUESTION # 50
Which migration solution should you recommend for Project1?
- A. From the Exchange admin center, start a migration and select Remote move migration
- B. From Exchange Online PowerShell, run the New-MaiboxExportRequest cmdlet.
- C. From Exchange Online PowerShell, run the New-MaiboxImportRequest cmdlet.
- D. From the Microsoft 365 admin center, start a data migration and click Upload PSST as the data service.
Answer: A
Explanation:
During Project1, some users will have mailboxes in Microsoft 365 and some users will have mailboxes in Exchange on-premises. To enable users be able to exchange email messages successfully during Project1 by using their current email address, we'll need to configure hybrid Exchange.
To migrate mailboxes in a hybrid Exchange configuration, you use Exchange admin center perform Remote move migrations.
Reference:
https://docs.microsoft.com/en-us/exchange/hybrid-deployment/move-mailboxes
Topic 1, Fabrikam, Inc
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication.
Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as a DNS server.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams & Skype for Business will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
Microsoft Office 365 ProPlus applications must be installed from a network share only.
Disruptions to email address must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online.
The installation of feature updates for Office 365 ProPlus must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The memberships of UserLicenses must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
NEW QUESTION # 51
Your network contains an on-premises Active Directory domain that syncs to Azure Active Directory (Azure AD).
The on-premises network contains a Microsoft SharePoint Server 2019 farm.
The company purchases a Microsoft 365 subscription.
You have the users shown in the following table
You plan to assign User1 and User2 the required roles to run the SharePoint Hybrid Configuration Wizard.
User1 will be used for on-premises credentials and User2 will be used for cloud credentials.
You need to assign the correct role to User2. The solution must use the principle of least privilege.
Which role should you assign to User2?
- A. Application administrator
- B. SharePoint farm administrator
- C. SharePoint administrator
- D. Global administrator
Answer: D
Explanation:
To run the SharePoint Hybrid Configuration Wizard, you need to provide credentials of a user (in this case User2) of a Global Administrator account in Azure Active Directory.
Reference:
https://www.c-sharpcorner.com/article/sharepoint-2019-enable-hybrid-experience/
NEW QUESTION # 52
You are confirming an enterprise application named Test App in Microsoft Azur as shown in the following exhibit.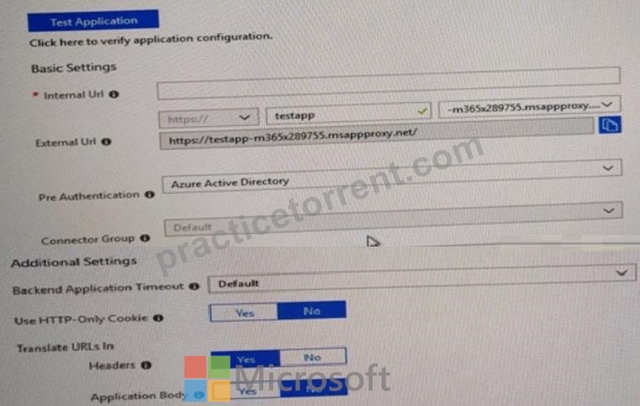
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 53
You need to add the custom domain names to Office 365 to support the planned changes as quickly as possible.
What should you create to verify the domain names successfully?
- A. three text (TXT) records
- B. three alias (CNAME) records
- C. one text (TXT) record
- D. one alias (CNAME) record
Answer: A
Explanation:
Section: [none]
Explanation:
Contoso plans to provide email addresses for all the users in the following domains:
* East.adatum.com
* Contoso.adatum.com
* Humongousinsurance.com
To verify three domain names, you need to add three TXT records.
Reference:
https://docs.microsoft.com/en-us/office365/admin/setup/add-domain?view=o365-worldwide Testlet 3 Case study This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Overview
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication.
Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as a DNS server.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
* Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft
365.
* Project2: After the successful completion of Project1, Microsoft Teams & Skype for Business will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
* All users must be able to exchange email messages successfully during Project1 by using their current email address.
* Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
* A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
* Microsoft 365 Apps for enterprise applications must be installed from a network share only.
* Disruptions to email access must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
* An on-premises web application named App1 must allow users to complete their expense reports online.
App1 must be available to users from the My Apps portal.
* The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
* After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
* The memberships of UserLicenses must be validated monthly. Unused user accounts must be removed from the group automatically.
* After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
* The principle of least privilege must be used.
NEW QUESTION # 54
You work at a company named Contoso, Ltd.
Contoso has a Microsoft 365 subscription that is configured to use the DNS domains shown in the following table.
Contoso purchases a company named Fabrikam, Inc.
Contoso plans to add the following domains to the Microsoft 365 subscription:
fabrikam.com
east.fabrikam.com
west.contoso.com
You need to ensure that the devices in the new domains can register by using Autodiscover.
How many domains should you verify, and what is the minimum number of enterpriseregistration DNS records you should add? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/windows-enroll
NEW QUESTION # 55
Your network contains two on-premises Active Directory forests named contoso.com and fabrikam.com. Fabrikam.com contains one domain and five domain controllers. Contoso.com contains the domains shown in the following table.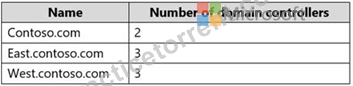
You need to sync all the users from both the forests to a single Azure Active Directory (Azure AD) tenant by using Azure AD Connect.
What is the minimum number of Azure AD Connect sync servers required?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
Explanation:
You can have only one active Azure AD Connect server synchronizing accounts to a single Azure Active Directory (Azure AD) tenant. You can have 'backup' Azure AD Connect servers, but these must be running in 'staging' mode. Staging mode means the Azure AD Connect instance is not actively synchronizing users but is ready to be bought online if the active Azure AD Connect instance goes offline.
When you have multiple forests, all forests must be reachable by a single Azure AD Connect sync server. The server must be joined to a domain. If necessary, to reach all forests, you can place the server in a perimeter network (also known as DMZ, demilitarized zone, and screened subnet).
References:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/plan-connect-topologies#multiple-forests-single-azure-ad-tenant
NEW QUESTION # 56
Your company has offices in several cities and 100.000 users.
The network contains an Active Directory domain contoso.com.
You purchase Microsoft 365 and plan to deploy several Microsoft 365 services.
You are evaluating the implementation of pass-through authentication and seamless SSO. Azure AD Connect will NOT be in staging mode.
You need to identify the redundancy limits for the planned implementation.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.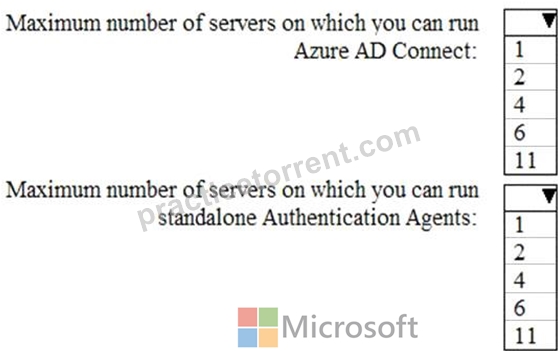
Answer:
Explanation:
Explanation
Azure AD Connect can be active on only one server. You can install Azure AD Connect on another server for redundancy but the additional installation would need to be in Staging mode. An Azure AD connect installation in Staging mode is configured and ready to go but it needs to be manually switched to Active to perform directory synchronization.
Azure authentication agents can be installed on as many servers as you like.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-pta-quick-start
NEW QUESTION # 57
You need to meet the application requirements for the Office 365 ProPlus applications.
You create an XML files that contains the following settings.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1:
Office 365 ProPlus feature updates will be installed twice a year in March and September.
The Channel element in the configuration file is set to 'Targeted'. This means Semi-Annual Targeted.
To help your organization prepare for a Semi-Annual Channel release, Microsoft provides Semi-Annual Channel (Targeted). The primary purpose of this update channel is to give pilot users and application compatibility testers in your organization a chance to work with the upcoming Semi-Annual Channel release Box 2:
Microsoft Office 365 ProPlus applications must be installed from a network share only.
The AllowCDNFallback value is currently set to true. The purpose of this setting is to enable Office 365 to be downloaded from Microsoft's Content Delivery Network if the network share is unavailable. The AllowCDNFallback value should be set to false to meet the technical requirement.
Reference:
https://docs.microsoft.com/en-us/deployoffice/configuration-options-for-the-office-2016-deployment-tool#updates-element
https://docs.microsoft.com/en-us/deployoffice/overview-of-update-channels-for-office-365-proplus
NEW QUESTION # 58
You need to configure the Office 365 service status notifications and limit access to the service and feature updates. The solution must meet the technical requirements.
What should you configure in the Microsoft 365 admin center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, table Description automatically generated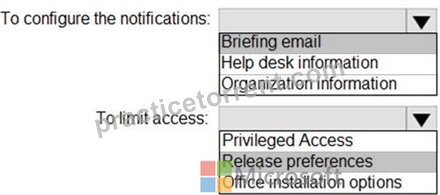
Reference:
https://docs.microsoft.com/en-us/briefing/be-admin
https://docs.microsoft.com/en-us/microsoft-365/admin/manage/release-options-in-office-365?view=o365-worldw
NEW QUESTION # 59
Your network contains an Active Directory domain and a Microsoft Azure Active Directory (Azure AD) tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct select ion is worth one point.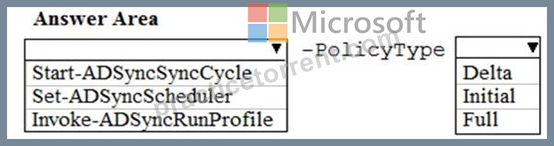
Answer:
Explanation:
Reference:
https://blogs.technet.microsoft.com/rmilne/2014/10/01/how-to-run-manual-dirsync-azure-active-directory-sync-updates/
NEW QUESTION # 60
You are developing a single-page application (SPA) that authenticates users by using MSALjs. The SPA must meet the following requirements:
* Only allow access to the users in an organization named contoso.onmicrosoft.com.
* Support single sign-on (SSO) across tabs and user sessions.
How should you complete the code for the SPA? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 61
Your network contains two Active Directory forests. Each forest contains two domains.
You plan to configure Hybrid Azure AD join for the computers.
You create a Microsoft Azure Active Directory (Azure AD) tenant.
You need to ensure that the computers can discover the Azure AD tenant.
What should you create?
- A. a new service connection point (SCP) for each domain
- B. a new service connection point (SCP) for each forest
- C. a new computer account for each computer
- D. a new trust relationship for each forest
Answer: B
Explanation:
Section: [none]
Explanation:
Your devices use a service connection point (SCP) object during the registration to discover Azure AD tenant information. In your on-premises Active Directory instance, the SCP object for the hybrid Azure AD joined devices must exist in the configuration naming context partition of the computer's forest. There is only one configuration naming context per forest. In a multi-forest Active Directory configuration, the service connection point must exist in all forests that contain domain-joined computers.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/devices/hybrid-azuread-join-manual
NEW QUESTION # 62
Your network contains an on-premises Active Directory domain. The domain contains a server named Server1. Server1 has a share named Share1 that contains the files shown in the following table.
You have a hybrid deployment of Microsoft 365.
You create a Microsoft SharePoint site collection named Col lection1.
You plan to migrate Share1 to a document library in Collection1
You configure the SharePoint Migration Tool as shown in the exhibit. (Click the Exhibit tab.) For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Answer:
Explanation:
Explanation
.
Box 1: No
File1.txt will not be migrated as it was created before Jan 1 2019
Box 2: Yes
File2.txt will be migrated as it was created after Jan 1 2019 and was modified after Mar 1 2019.
Box 3: Yes
File permissions will be maintained after the migration.
References:
https://docs.microsoft.com/en-us/sharepointmigration/spmt-settings
NEW QUESTION # 63
You have the Microsoft Azure Active Directory (Azure AD) users shown in the following table.
Your company uses Microsoft Intune.
Several devices are enrolled in Intune as shown in the following table.
The device compliance policies in Intune are configured as shown in the following table.
You create a conditional access policy that has the following settings:
The Assignments settings are configured as follows:
- Users and groups: Group1
- Cloud apps: Exchange Online
- Conditions: Include All device state, exclude Device marked as compliant Access controls is set to Block access.
For each of the following statements, select yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/conditions
NEW QUESTION # 64
You are evaluating the use of multi-factor authentication (MFA).
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-mfa-policy
https://blog.admindroid.com/configuring-and-managing-mfa-in-office-365/
NEW QUESTION # 65
You company has a Microsoft 365 subscription that contains the domains shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://support.office.com/en-gb/article/what-do-domain-statuses-mean-in-office-365-3ecf1fef-3b31-497c-98bc-e57e2413b4e5
NEW QUESTION # 66
Your company is based in the United Kingdom (UK).
Users frequently handle data that contains Personally Identifiable Information (PII).
You create a data loss prevention (DLP) policy that applies to users inside and outside the company. The policy is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based in the information presented in the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
The text in the Policy Settings section of the exhibit explains what will happen.
If a user sends between 1 and 10 instances of the sensitive info (passport number), then a notification email and will be sent to the user and a policy tip will be displayed. The email will not be blocked though. Therefore, it will be allowed.
If a user sends more than 10 instances of the sensitive info (passport number), the email will be blocked and a high-severity alert generated. However, the user can override the block.
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/data-loss-prevention-policies
NEW QUESTION # 67
......
Microsoft MS-100 exam covers a wide range of topics, including configuring and managing Azure AD, implementing and managing hybrid identities, managing user roles and access, configuring security and compliance features, and managing Microsoft 365 governance and administration. MS-100 exam also covers the deployment and management of Microsoft 365 services such as Exchange Online, SharePoint Online, Teams, and OneDrive.
MS-100 Dumps Full Questions with Free PDF Questions to Pass: https://www.practicetorrent.com/MS-100-practice-exam-torrent.html
Free Microsoft 365 MS-100 Official Cert Guide PDF Download: https://drive.google.com/open?id=1bkNoXuIPTVleXz5ODdtnxDGzMbG8Cg4Y