

ISACA Certified Information Systems Auditor (CISA中文版) : CISA 中文
- Exam Code: CISA-CN
- Exam Name: Certified Information Systems Auditor (CISA中文版)
- Updated: Oct 16, 2026 Q & A: 1605 Questions and Answers

 PDF Version Demo

PC Test Engine
ISACA CISA 中文 Value Pack (Frequently Bought Together)

- If you purchase ISACA CISA 中文 Value Pack, you will also own the free online test engine.
- PDF Version + PC Test Engine + Online Test Engine
- Value Pack Total: $119.98 $79.99
About ISACA CISA 中文 Exam
From a free demo to downloadable practice files, browser-based testing, and checkout supported by McAfee security services, PracticeTorrent brings the key CISA 中文 preparation tools together in one place. Candidates for ISACA Certified Information Systems Auditor (CISA中文版) can use the 1605 practice questions to plan, test, and revisit their knowledge in 2026.
ISACA CISA 中文 Exam Overview:
| Certification Vendor: | ISACA |
|---|---|
| Exam Name: | Certified Information Systems Auditor |
| Exam Number: | CISA |
| Exam Duration: | 240 minutes |
| Exam Format: | Multiple Choice |
| Real Exam Qty: | 150 |
| Passing Score: | 450 |
| Certificate Validity Period: | 3 Years (requires 120 CPE credits) |
| Exam Price: | USD 575 (Member) / USD 760 (Non-Member) |
| Related Certifications: | Certified Information Security Manager (CISM) Certified in Risk and Information Systems Control (CRISC) Certified Information Systems Auditor (CISA) |
| Available Languages: | Spanish, Korean, French, English, Turkish, Chinese Simplified, German, Italian, Japanese, Chinese Traditional |
| Sample Questions: |  |
| Exam Way: | Online Remote Proctored or In-person at PSI Testing Centers |
| Pre Condition: | 5 years of professional information systems auditing, control or security work experience. Substitutions and waivers of such experience may be obtained. |
| Official Syllabus URL: | https://www.isaca.org/credentialing/cisa |
ISACA CISA 中文 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Governance and Management of IT | 18% | - IT Governance
|
| Information Systems Acquisition, Development and Implementation | 12% | - Information Systems Acquisition and Development
|
| Information Systems Operations and Business Resilience | 26% | - Business Resilience
|
| Information Systems Auditing Process | 18% | - Execution
|
| Protection of Information Assets | 26% | - Security Event Management
|
ISACA CISA 中文 Certification Exam FAQ
The CISA 中文 exam, Certified Information Systems Auditor (CISA中文版), assesses whether a candidate can apply ISACA knowledge to the skills measured by this credential. It is associated with the Certified Information Systems Auditor certification. The certification is positioned at the Professional level. Related credentials include Certified Information Systems Auditor (CISA), Certified Information Security Manager (CISM), Certified in Risk and Information Systems Control (CRISC).
The CISA 中文 exam includes 150 questions and allows 240 minutes. Plan your pacing before exam day rather than calculating it under pressure. Timed sessions with PracticeTorrent practice tests can help you decide when to flag a difficult item, keep moving, and reserve enough time for a final review.
The published passing score for ISACA Certified Information Systems Auditor (CISA中文版) is 450, and the official exam fee is USD 575 (Member) / USD 760 (Non-Member). A retake requires budgeting for the full official fee again, so it is sensible to complete several timed practice tests before scheduling. Consistent results across the 1605 practice questions can give you a clearer picture of your readiness.
The stated prerequisite information for ISACA Certified Information Systems Auditor (CISA中文版) is: 5 years of professional information systems auditing, control or security work experience. Substitutions and waivers of such experience may be obtained. Before registering, review the eligibility details on the official exam page to confirm the requirements.
Yes. PracticeTorrent provides a free PDF demo so you can review the format and quality of the ISACA Certified Information Systems Auditor (CISA中文版) practice questions before placing an order. Your purchase includes 365 days of free updates, and you can extend the update service after expiration at a 50% discount.
If you take the corresponding CISA 中文 exam within 60 days of purchase and do not pass, you may apply for a full refund under the 100% Money Back Guarantee. Claims based on an exam taken within 3 days of purchase are not eligible; free materials, expired orders, and downloaded products that were not used before sitting for the exam are also excluded. The candidate name must match the payer name.
To apply, submit a scanned enrollment slip and the official Score Report PDF within 2 days after the exam. Eligible requests are processed within 7 days. If you prefer an alternative, you may receive two free products of equal value and keep the update service for your original purchase.
Delivery is instant after payment. Your download is also sent to your email within one minute; if it has not arrived within 2 hours, contact customer service. There is no limit on the number of computers on which the material can be installed.
The published ISACA Certified Information Systems Auditor (CISA中文版) outline contains 5 major domains. The opening domains include:
- Governance and Management of IT (18%)
- Information Systems Auditing Process (18%)
- Protection of Information Assets (26%)
Review the complete Exam Topics section above for every domain and subtopic before planning your study time.
ISACA Certified Information Systems Auditor (CISA中文版) Sample Questions:
下列何者最能證明IT組合管理的有效性?
- A. IT 組合會隨著業務策略的變化而更新。
- B. IT 組合根據目前行業基準進行更新。
- C. IT 組合中的專案依業務職能進行優先排序。
- D. IT 組合更新在獲得批准後會進行溝通。
Correct Answer: A 🗳️
資訊系統審計師發現,某個組織的系統經常被用於加密貨幣挖礦。下列哪一項是審計師的首要行動方案?
- A. 建議更改組織的防火牆設定。
- B. 立即報告該事件。
- C. 請查閱組織的可接受使用政策。
- D. 要求卸載挖礦軟體。
Correct Answer: C 🗳️
下列哪一項是最大限度降低公司遺失的行動裝置被未經授權存取風險的最佳控制措施?
- A. 裝置加密
- B. 密碼/PIN碼保護
- C. 裝置追蹤軟體
- D. 定期備份
Correct Answer: A 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
就IT治理而言,價值交付的首要目標是:
- A. 優化投資。
- B. 提高效率。
- C. 確保合規。
- D. 推廣最佳實踐
Correct Answer: A 🗳️
Explanation: Only visible for PracticeTorrent members. You can sign-up / login (it's free).
某組織準備實施一套包含多個模組的全新IT解決方案。最後一個模組負責將處理後的資料更新到資料庫中。下列哪一項發現最應引起資訊系統審計師的注意?
- A. 缺乏正式的變更審核流程
- B. 缺少資料字典
- C. 缺少輸入驗證
- D. 使用弱加密
Correct Answer: C 🗳️
Viewing page 1 out of 321 pages.
Viewing questions 1-5 out of 1605 questions.


Related Exams
Related Certifications
Over 81356+ Satisfied Customers
Popular Vendors
What Clients Say About Us
Why Choose Us
-
QUALITY AND VALUE
PracticeTorrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
-
TESTED AND APPROVED
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
-
EASY TO PASS
If you prepare for the exams using our PracticeTorrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
-
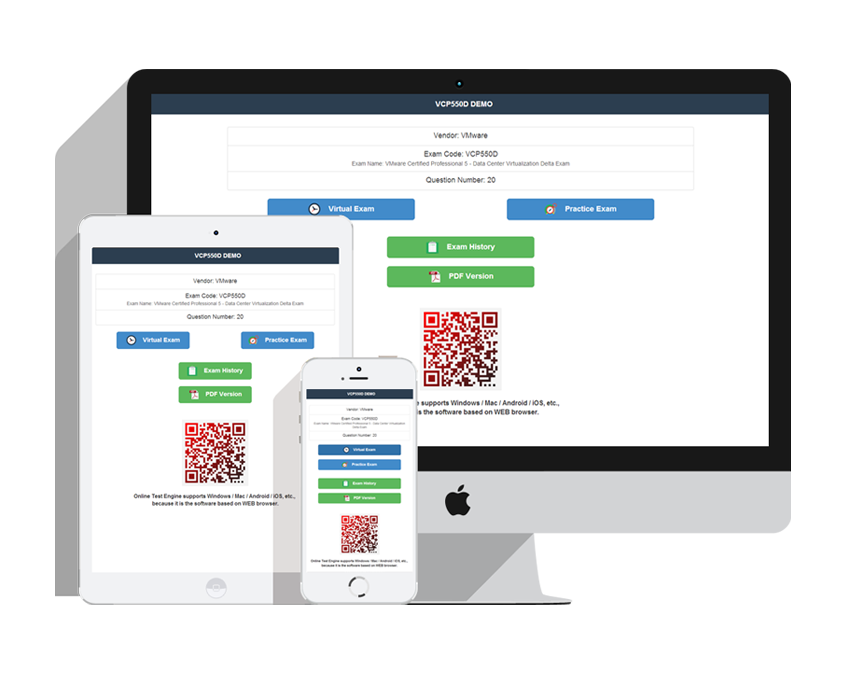
TRY BEFORE BUY
PracticeTorrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
Our Clients




Get the high score and achieve the certification with our latest practice torrent. The complete exam prep torrent contains the questions & answers which are related to the actual test. You can pass your actual test at first attempt.
Tags
- FCSS_NST_SE-7.6 practice torrentMay 28, 2022
- CRISC practice torrentMay 28, 2022
- 303-300 practice torrentMay 28, 2022
- NSE7_SOC_AR-7.6 practice torrentMay 28, 2022
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PracticeTorrent NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy