

GAQM ISO 27001 ISMS - Certified Internal Auditor : ISO-ISMS-CIA
- Exam Code: ISO-ISMS-CIA
- Exam Name: ISO 27001 ISMS - Certified Internal Auditor
- Updated: Sep 30, 2026 Q & A: 0 Questions and Answers

 PDF Version Demo

We are already working hard to make ISO-ISMS-CIA exam material available to our valued customers. If you are interested in ISO-ISMS-CIA exam material, provide us your email and we will notify you.
GAQM ISO-ISMS-CIA Value Pack (Frequently Bought Together)

- If you purchase GAQM ISO-ISMS-CIA Value Pack, you will also own the free online test engine.
- PDF Version + PC Test Engine + Online Test Engine
About GAQM ISO-ISMS-CIA Exam
To qualify for the GAQM ISO-ISMS-CIA Certification Exam, individuals must have a minimum of two years' experience in conducting internal audits of ISMS or have completed an ISO 27001 Lead Auditor training course. ISO 27001 ISMS - Certified Internal Auditor certification exam consists of 80 multiple-choice questions, which need to be completed in 120 minutes. ISO-ISMS-CIA exam covers various topics, including ISMS requirements, risk management, internal audit management, and reporting findings.
Free demos before purchase
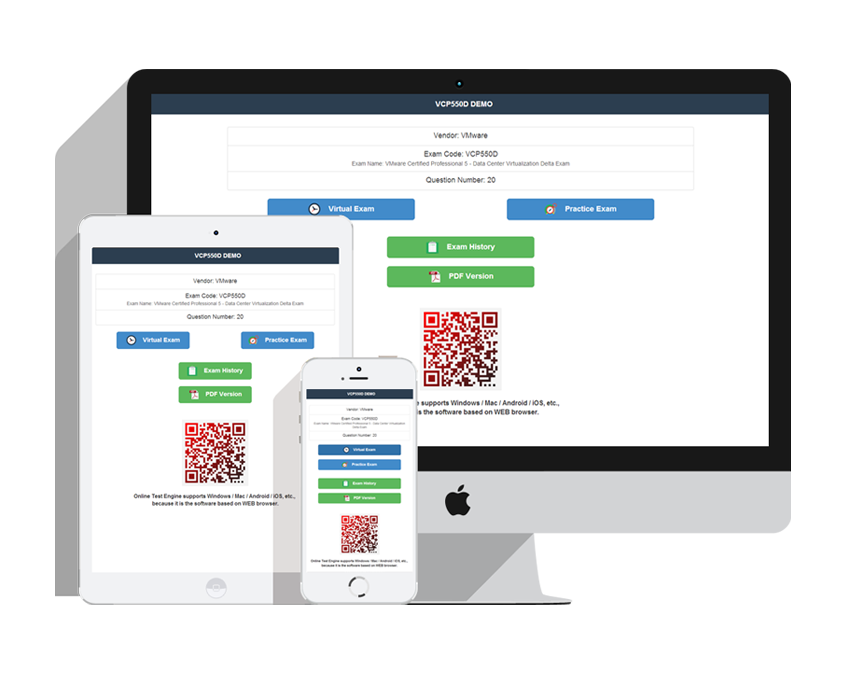
You may hesitate whether to take our software, or you're worry about it's worthy of buying it. It's easy to ensure your heart. We provide three different versions of GAQM: ISO ISO 27001 ISMS - Certified Internal Auditor free practice demos (PDF/PC Test Engine/Online Test Engine) for you, freely. It's simple and convenient for you to get the demos, just click our links on the product page. These ISO 27001 ISMS - Certified Internal Auditor demos will show you our whole style and some test question for you. If you are satisfactory with our model, you can pay for it then our system will send you the ISO 27001 ISMS - Certified Internal Auditor practice dumps within ten minutes.
The ISO 27001 ISMS - Certified Internal Auditor Exam is a proctored online exam that consists of 100 multiple-choice questions. ISO-ISMS-CIA exam duration is 2 hours, and candidates need to score a minimum of 70% to pass the exam. ISO-ISMS-CIA exam content covers various topics such as the principles of information security management, risk management, asset management, incident management, and compliance with legal and regulatory requirements.
The ISO-ISMS-CIA certification is suitable for professionals who are responsible for auditing an organization's ISMS, including internal auditors, information security managers, compliance officers, and consultants. ISO 27001 ISMS - Certified Internal Auditor certification is also beneficial for individuals seeking a career in information security auditing as it enhances their credibility and provides them with a competitive edge in the job market. Overall, the GAQM ISO-ISMS-CIA certification exam is an excellent opportunity for individuals to enhance their knowledge and skills in auditing an organization's ISMS and to validate their expertise in the field of information security.
Secure payment
We always attach high importance of our clients' benefit. For your property safety visiting and buy our ISO-ISMS-CIA : ISO 27001 ISMS - Certified Internal Auditor valid pdf torrent, we cooperate with the well-known reputation platform like Credit Card to receive your payment. So don't worry you'll lose your money. You can use your credit card which suitable for Credit Card. Choose our ISO 27001 ISMS - Certified Internal Auditor sure pass torrent, you will 100% pass.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Man struggles up wards. People desire for higher positions, so they should study hard and try to attain the ISO 27001 ISMS - Certified Internal Auditor certification for what they want. But there are exactly many barriers on the way you forward. You want a higher position in the industry, so you want to pass the ISO 27001 ISMS - Certified Internal Auditor exam, however, you feel boring, tired and fruitless when you prepare for your exam. Undoubtedly, it is the barrier separates you and your important ISO 27001 ISMS - Certified Internal Auditor certification. Play a leading role of worldwide certification dumps, we'll help you clear all the barriers in your road to pass the GAQM: ISO ISO 27001 ISMS - Certified Internal Auditor actual exam. We are able to make your study more acceptable, more interesting and happier. We stand behind you, support you to pass the exam. It's absolutely convenient. Apply our ISO 27001 ISMS - Certified Internal Auditor latest practice pdf, you can study in everywhere and everyplace you want with your mobile phone. It's not necessary for you to spend a lot of time to practice the ISO-ISMS-CIA free study torrent and you're able to study just in your short leisure time. The certificate will be sent to your pocket after only 20~30 hours study with GAQM ISO 27001 ISMS - Certified Internal Auditor sure pass torrent by our examination database. Once you purchase, our system will send you the subjects by email instantly. Furthermore our professional team will checks and updates our software frequently. That is to say, we'll send you the newest and updated ISO 27001 ISMS - Certified Internal Auditor valid pdf torrent to you within one year after purchase. And over a year, we will give you the priority of half-off for buying our products and send you different discount activities information about our GAQM: ISO ISO 27001 ISMS - Certified Internal Auditor latest practice pdf. In addition, our team is famous for our high passing rate which up to 99%, so you completely needn't worry about our quality. Moreover, you can apply for full refund with your ISO 27001 ISMS - Certified Internal Auditor failed certification if you failed in your exam or change any other version of our products. Actually, we devotes ourselves the purpose of customers first, and we ensure you'll get what you want without a little bit of regret after choose us ISO 27001 ISMS - Certified Internal Auditor training torrent. You trust us, we return you the victory.

GAQM ISO-ISMS-CIA certification is an excellent credential for professionals who want to become certified internal auditors for ISO 27001 Information Security Management System (ISMS). ISO 27001 ISMS - Certified Internal Auditor certification process involves a rigorous exam that tests the candidate's expertise in various aspects of ISMS and internal auditing. A certified internal auditor with ISO-ISMS-CIA certification can help organizations identify security vulnerabilities, assess risks, and develop effective security controls to protect their sensitive data and information.
GAQM ISO-ISMS-CIA Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Information Security Controls | - Control Implementation
|
| Internal Audit Principles | - Audit Fundamentals
|
| ISO 27001 Requirements | - ISMS Clauses
|
| Risk Assessment and Risk Treatment | - Risk Management Activities
|
| Compliance and Governance | - Regulatory and Organizational Requirements
|
| Conducting Internal Audits | - Audit Process
|
| Audit Reporting and Follow-Up | - Audit Results Management
|
| Fundamentals of Information Security Management Systems | - ISMS Concepts
|


Related Exams
Related Certifications
Over 81356+ Satisfied Customers
What Clients Say About Us
Why Choose Us
-
QUALITY AND VALUE
PracticeTorrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
-
TESTED AND APPROVED
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
-
EASY TO PASS
If you prepare for the exams using our PracticeTorrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
-
TRY BEFORE BUY
PracticeTorrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
Our Clients




Get the high score and achieve the certification with our latest practice torrent. The complete exam prep torrent contains the questions & answers which are related to the actual test. You can pass your actual test at first attempt.
Tags
- SC-100J practice torrentMay 28, 2022
- Data-Cloud-Consultant practice torrentMay 28, 2022
- JN0-106 practice torrentMay 28, 2022
- PMP-Deutsch practice torrentMay 27, 2022
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PracticeTorrent NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy